
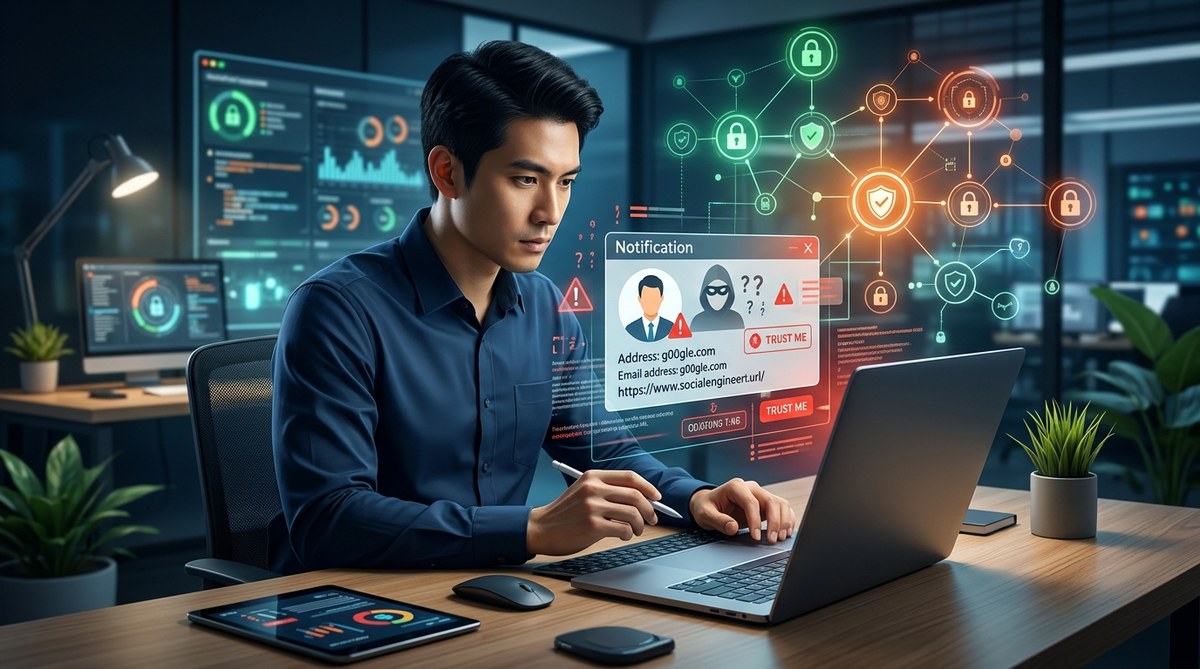
A colleague stops you in the hallway. They look stressed. They say the CEO needs a password reset right now, and they forgot their badge. Your instinct says help. But something feels off. That feeling is your first clue. Social engineering attacks don’t look like a hooded figure typing in a dark room. They look like everyday interactions. A friendly phone call. An urgent email. A person in a uniform you don’t recognize. By the time the damage is done, the attacker is already gone. The good news is that these attacks leave traces. Once you know the signs of social engineering attacks, you can stop them cold.
Social engineering attacks exploit human trust, not technical flaws. The hidden signs include unnatural urgency, requests that bypass normal procedure, and subtle emotional pressure. By training your team to spot these red flags, you can prevent breaches that bypass firewalls and antivirus software entirely. Awareness is your strongest defense.
What makes social engineering so hard to catch
Most people expect cyberattacks to involve strange code or a flashing warning screen. Social engineering is different. It targets the most human part of security: our willingness to help. Attackers study how your company communicates. They learn the names of your executives. They know when your help desk is busiest. They use that knowledge to slip through.
The real danger is that these attacks feel normal. An email from “IT support” asking you to verify your credentials looks just like the real thing. A phone call from “the vendor” sounds exactly like the person you spoke with last month. The signs of social engineering attacks are often buried in small details. A slight change in an email address. A request that comes from an unusual department. A tone of voice that pressures you to act fast.
The 5 hidden signs you should never ignore
These are the subtle clues that something is wrong. They are easy to miss when you are busy. But they are almost always present in a social engineering attempt.
1. An unnatural sense of urgency
Attackers want you to act before you think. They create a crisis that demands immediate action. Maybe your account will be locked in one hour. Maybe a package needs your confirmation right now. Maybe the boss is in a meeting and needs this information immediately.
Real emergencies in a workplace rarely come with that kind of pressure from someone you do not recognize. When you feel rushed, pause. That pause is your best defense.
2. A request that bypasses normal procedure
Your company has a process for password resets. Your IT team has a protocol for granting access. A social engineer will try to skip those steps. They will ask you to make an exception. They will say the normal process takes too long. They might claim they are a new hire and the system is down.
If someone asks you to break a rule, even a small one, treat it as a red flag. Legitimate requests follow the rules.
3. Emotional manipulation
Attackers play on your emotions. They might sound angry, scared, or desperate. A person pretending to be from your CEO’s office might sound frustrated and demanding. A fake vendor might sound panicked about a missed payment. They want you to feel sorry for them or intimidated by them.
When an interaction makes you feel emotionally charged, step back. Ask yourself if the emotion is being used to distract you.
4. Information that is almost right
A social engineer often has some details about you. They might know your name, your department, or the name of your manager. They use this to build trust. But the details are usually slightly wrong. They might mispronounce a name. They might reference a project that does not exist. They might say they are from a department that was renamed last year.
Pay attention to those small mismatches. They are often the only sign that something is fake.
5. Reluctance to verify their identity
A legitimate person will be happy to prove who they are. A social engineer will avoid verification. They will make excuses. Their phone might be broken. Their email is not working. They are in a hurry. They cannot send a photo of their ID.
Anyone who refuses to verify their identity should be treated with suspicion.
A practical process for verifying any request
When you spot one of those signs, use this three-step process. It takes less than a minute and can save your company from a major breach.
-
Stop and breathe. Do not act on the request immediately. Take three seconds to think. That alone can break the attacker’s spell.
-
Verify through a separate channel. Do not use the phone number or email address the person gave you. Use a contact method you already have on file. Call the main company number. Send an email to the official address. If the request is real, the person will understand.
-
Confirm the procedure. Ask yourself if this request follows your normal process. If it does not, escalate it to a manager or your security team.
Common social engineering techniques and their warning signs
The following table shows the most common techniques attackers use and the specific warning signs associated with each one.
| Technique | How it works | Warning sign to watch for |
|---|---|---|
| Phishing | Fake email that looks like it comes from a trusted source | Sender address has a slight typo or unusual domain |
| Vishing | Phone call pretending to be from support or a vendor | Caller insists on staying on the line while you act |
| Pretexting | Attacker creates a fake scenario to gain trust | They reference an event or person you cannot verify |
| Baiting | Attacker offers something tempting like a free download | The offer seems too good to be true or comes from a stranger |
| Tailgating | Attacker follows someone into a secure area | They are carrying items that make it hard to badge in |
What to do when you spot the signs
If you recognize any of these signs of social engineering attacks, do not ignore them. Here is what to do next.
- Report the incident to your security team immediately.
- Do not confront the person if you are in a physical space. Walk away and find a secure location.
- Save any emails, messages, or voicemails for investigation.
- Alert your colleagues so they do not fall for the same attack.
“Social engineering is not about hacking computers. It is about hacking people. The best defense is a team that knows how to say no politely and verify everything.” — Kevin Mitnick, cybersecurity expert
Common mistakes that make you an easier target
People often think they are too smart to be tricked. That confidence is exactly what attackers exploit. Here are common mistakes that make social engineering more effective.
- Assuming you can spot a scam based on intuition alone
- Trusting caller ID or email display names without checking the underlying details
- Feeling embarrassed to verify someone’s identity
- Thinking that only high level executives are targeted
- Letting politeness override security
The most dangerous mistake is thinking it will never happen to you. It can happen to anyone. The best defense is building good habits now.
How to train your team to spot these signs
Training is not a one time event. It needs to be part of your regular routine. Here are some practical ways to keep your team sharp.
- Run simulated phishing campaigns every quarter.
- Share real world examples of social engineering attacks and how they were caught.
- Reward employees who report suspicious activity instead of punishing them for being suspicious.
- Make verification a normal part of your culture. No one should feel awkward about asking for proof.
- Review your incident response plan regularly and include social engineering scenarios.
For a deeper look at building a security aware culture, read our guide on how to build a risk-aware culture that protects your business from the inside out.
Staying ahead of the attackers in 2026
Social engineering attacks are not going away. They are getting more sophisticated. Attackers now use AI to generate convincing voice clones and realistic emails. They scrape social media for personal details. They know more about you than ever before.
But the fundamentals of defense remain the same. Slow down. Verify. Trust your gut when something feels off. The signs of social engineering attacks are there. You just have to look for them.
Make it a habit to check the small details. Look at the email address, not just the name. Listen for urgency and emotion. Question requests that skip procedure. When you build these habits, you become the hardest target in your organization.
Your next step toward better security
Start today. Pick one of the warning signs from this article. Share it with a teammate. Talk about it during your next team meeting. Practice the three step verification process. The more you practice, the more natural it becomes.
You do not need to be a cybersecurity expert to stop a social engineering attack. You just need to pay attention and follow the process. That is how you protect yourself, your team, and your organization.
For more guidance on building a strong security posture, check out our article on top strategies to prevent phishing attacks and protect your digital identity.