
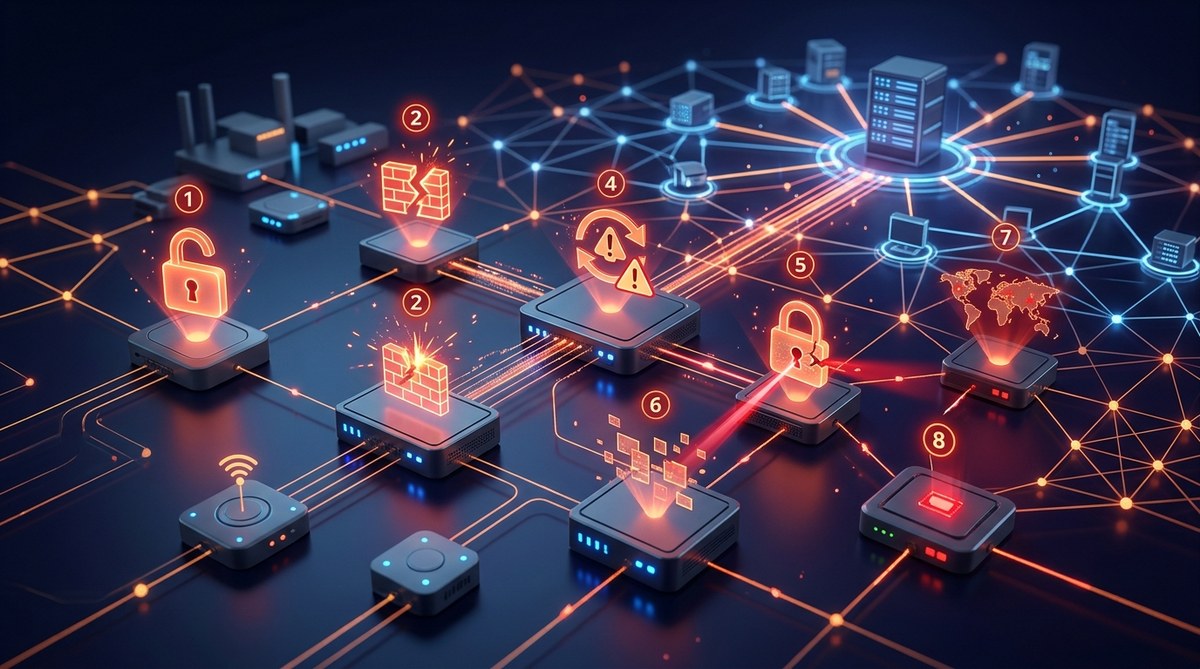
Picture this: you have a dozen smart sensors on a factory floor. Each one collects data, talks to a central system, and makes operations run smoothly. Now imagine one of those sensors has a default password that nobody changed. A hacker finds it, slips inside, and before you know it, they are moving laterally through your entire corporate network. That is the nightmare scenario of unsecured edge computing. Every device you push to the perimeter is a potential door. And in 2026, the number of those doors is growing faster than most teams can secure them.
Edge computing devices are often deployed with minimal security, making them prime targets for attackers. The eight vulnerabilities covered here include weak authentication, unpatched firmware, insecure APIs, and poor physical security. Each one can act as a bridge from a low-value sensor to your most sensitive data. The good news? You can close these gaps with the right strategy.
Why Edge Devices Are a Security Blind Spot
Edge computing brings processing closer to where data is generated. That is great for speed and bandwidth. But it also scatters your attack surface across dozens or hundreds of small, often overlooked devices. A single temperature sensor in a warehouse might have more access to your network than you realize.
The core problem is visibility. Many IT teams treat edge devices like appliances. Plug them in, let them run, forget about them. But these are full computers running operating systems, connecting to the cloud, and processing sensitive data. When you ignore them, you are handing attackers a foothold.
The 8 Critical Vulnerabilities You Need to Know
Here are the specific weaknesses that turn edge devices into entry points for network-wide breaches. If you manage distributed systems, this list is your checklist for 2026.
1. Weak or Default Authentication
It is shocking how many edge devices ship with credentials like “admin/admin” or “root/root.” Teams often skip changing them during setup. Automated scanners on the internet find these devices in minutes.
Attackers use these weak credentials to log in directly. Once inside, they can read data, install malware, or use the device as a jump point to other systems. This is one of the most common edge computing vulnerabilities because it is so easy to exploit.
2. Unpatched Firmware and Software
Edge devices rarely receive automatic updates. Many run on custom Linux builds that the vendor stops supporting after a year. If a critical vulnerability is discovered, you are stuck waiting for a manual patch that may never come.
In 2026, we see attackers specifically targeting known CVEs in edge routers, IoT gateways, and industrial controllers. If your firmware is six months old, you are exposed.
3. Insecure APIs and Communication Protocols
Edge devices talk to central servers using APIs. These APIs are often built for speed, not security. They might use HTTP instead of HTTPS, or skip authentication entirely.
A compromised API can let an attacker send fake data to your system, pull real data out, or inject commands. This is especially dangerous when edge devices control physical actions like locking doors or adjusting temperatures.
4. Lack of Encryption for Data at Rest and in Transit
Many edge devices store data locally before sending it upstream. If that data is not encrypted, a physical theft or a remote compromise gives the attacker everything. The same goes for data moving across the network. Without encryption, anyone on the same segment can eavesdrop.
This vulnerability is often ignored because encryption adds processing overhead. But the risk of exposing customer or operational data is far greater than the performance cost.
5. Poor Physical Security
Edge devices live in places you do not control. A sensor on a streetlight, a camera in a parking lot, a controller in an unsecured closet. Anyone with a screwdriver can access the USB port, swap the SD card, or connect a keyboard.
Physical access is total access. An attacker can clone the device, extract credentials, or plant a backdoor. This is a vulnerability that no amount of software patching can fix.
6. Insufficient Network Segmentation
This is the big one. Too often, edge devices sit on the same flat network as critical servers and workstations. A compromised sensor can then reach your database, your Active Directory, or your backup systems.
Network segmentation is the simplest way to contain edge computing vulnerabilities. If the sensor can only talk to a single gateway, a breach stays in the sensor. Without segmentation, a single weak device opens the door to everything.
7. Outdated or Missing Security Monitoring
Edge devices rarely have agents or logging enabled. They run minimal software, so IT teams do not install endpoint protection. That means no one sees the attack happening.
An attacker can live on an edge device for months, using it to scan your internal network or exfiltrate data in small chunks. Without monitoring, you will never know until the real damage is done.
8. Vendor Lock-In and Abandonment
Many edge device vendors go out of business or stop supporting older models. When that happens, you are left with devices that never receive security updates. You cannot patch them, and replacing them is expensive.
This is a supply chain risk that directly creates edge computing vulnerabilities. If your vendor disappears, your devices become ticking time bombs.
A Practical Process for Closing Edge Gaps
You cannot fix everything at once. Here is a numbered process to prioritize your efforts.
- Inventory every edge device on your network. Use a scanning tool or a simple spreadsheet. Know the make, model, firmware version, and location of each one.
- Classify devices by risk. A sensor in a locked server room is lower risk than a camera in a public lobby. Focus on the highest exposure first.
- Change all default credentials immediately. Use strong, unique passwords or certificate-based authentication where possible.
- Segment your network. Put edge devices on a separate VLAN with strict firewall rules. They should only talk to specific servers, not the whole network.
- Enable logging and monitoring. Even if you cannot install an agent, forward syslog data to a central SIEM. Watch for unusual traffic patterns.
- Establish a patching cadence. Check for firmware updates monthly. If a vendor stops supporting a device, plan for replacement within a quarter.
- Document your vendor risk. Include security support terms in your procurement process. Do not buy devices from companies that cannot commit to updates.
Common Mistakes That Widen the Door
Even well-intentioned teams make these errors. Avoid them.
| Mistake | Why It Hurts |
|---|---|
| Using the same password for all edge devices | One breach compromises everything |
| Allowing edge devices to initiate outbound connections to the internet | Opens a direct tunnel for data exfiltration |
| Skipping physical security reviews | A stolen device can reveal network keys |
| Treating edge devices as “set and forget” | Vulnerabilities grow over time |
| Not testing vendor security claims | Some devices ship with known backdoors |
Expert Advice on Managing Edge Risk
“The biggest mistake I see is treating edge devices as too simple to matter. They are not. Every device on your network is a potential entry point. If you cannot patch it, monitor it, or segment it, you need to remove it. There is no middle ground.” – Senior Network Architect, industrial security firm
That advice holds true in 2026 more than ever. As edge deployments grow, the margin for error shrinks.
How to Scan Your Environment Today
Here is a bulleted list of actions you can take this week to identify edge computing vulnerabilities in your own environment.
- Run a network scan to discover all connected devices. Look for unknown or unmanaged endpoints.
- Check each device for default credentials. Try “admin/admin” on a test device to see how easy it is.
- Review firewall rules. Are edge devices allowed to reach the internet or internal servers?
- Verify firmware versions against the vendor’s latest release.
- Check if data is encrypted in transit. Use a packet capture tool to inspect traffic from a sample device.
- Look at physical locations. Which devices are accessible to unauthorized people?
Building a Long-Term Edge Security Strategy
Fixing individual vulnerabilities is good, but you need a system. Start with a solid risk assessment framework to evaluate each device class. Then avoid the common pitfalls outlined in common risk management mistakes.
For teams just starting, a practical risk register can track each device’s vulnerabilities and remediation status. And when you need to decide between patching and replacing, understanding residual risk helps you make the call.
Edge security is not a one-time project. It is an ongoing practice. The devices change, the threats evolve, and your strategy must keep pace.
Your Next Move: Turning Knowledge Into Action
You now know the eight critical edge computing vulnerabilities that open the door for network-wide breaches. You have a process to fix them, a list of mistakes to avoid, and expert advice to guide you.
The real work starts when you close this page. Pick one device on your network today. Check its credentials. Review its firmware. Look at what it can reach. That single action could be the difference between a secure network and a costly breach. Stay prepared, stay aware, and keep those doors locked.